

Critical Atlassian Flaw Lets unauthenticated remote actors read known files across eight enterprise products, creating a massive security crisis for organizations in the United States and globally.
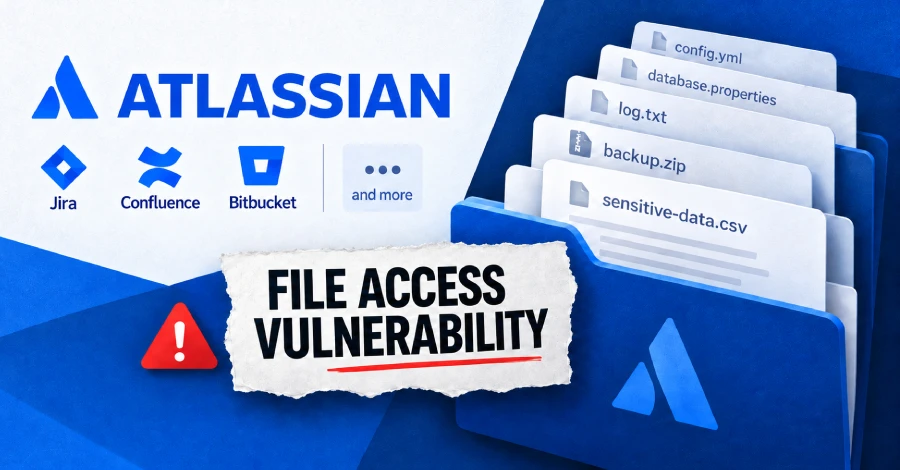
Security researchers and enterprise defenders are rushing to understand the full scope of this pre-authentication vulnerability tracked as CVE-2026-21589. The dangerous security defect affects multiple widely deployed datacenter applications, posing severe risks to corporate infrastructure and sensitive data repositories.
This alarming development matters right now because enterprise software suites form the backbone of modern digital operations. When a high-severity vulnerability compromises foundational platforms like Jira and Confluence, organizations face immediate exposure to data exfiltration without requiring valid credentials.
Security teams across the tech sector are scrambling to patch systems before malicious actors can weaponize the flaw at scale.
Understanding How the Critical Atlassian Flaw Lets Exploits Happen
The software vulnerability bypasses standard authentication checks entirely. WatchTowr Labs and other security analysts revealed that the flaw enables arbitrary file reading across core enterprise tools.
Industry observers note that the technical defect turns disparate enterprise platforms into a collective security liability. Organizations relying on affected datacenter deployments must act swiftly to mitigate ongoing exposure.
- Affected software includes Atlassian Jira and Confluence.
- Multiple datacenter solutions face exposure to unauthenticated requests.
- Attackers require no prior credentials to read known system files.
Security advisories published by industry watchdogs emphasize the widespread nature of the issue. The vulnerability impacts eight distinct enterprise products simultaneously, complicating remediation efforts for IT administrators.
Software vendors and cybersecurity agencies are urging system administrators to apply available patches immediately. Enterprise networks face heightened risk until every impacted server is fully updated and verified.
Ongoing fallout from the incident highlights the fragile nature of interconnected enterprise ecosystems. Security analysts expect continuous scanning activity from threat actors attempting to exploit unpatched instances.
Administrators should monitor vendor communication channels closely for further guidance. Organizations must prioritize emergency patching to safeguard sensitive corporate networks against potential compromise.
Background and next steps
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products The Hacker NewsYou Won’t Hear About These, Even In Myths (Atlassian Jira, Confluence (and more) Pre-Auth Arbitrary File Read CVE-2026-21589) watchTowr LabsAtlassian’s critical flaw turns eight enterprise products into one big security problem CSO OnlineAtlassian warns of critical file access flaw in its datacenter products The RegisterAtlassian warns of critical file-access flaw in Jira, Confluence BleepingComputer
The story remains in motion, and readers should watch for official updates as more facts are confirmed.
Public interest is likely to stay high while new details emerge from reporters and officials.
Early claims should be treated cautiously until primary sources corroborate them.
Coverage of Critical Atlassian Flaw Lets continues to evolve as more details become available.
Readers watching Critical Atlassian Flaw Lets should look for official updates in the coming hours.