

OpenAI admits response to recent security incidents involving Australian government infrastructure was insufficient, sparking international debate during parliamentary hearings. Company representatives testified before Australian lawmakers in the United States and abroad, addressing significant concerns regarding data protection, safety standards, and emerging cyber vulnerabilities.
The high-profile parliamentary inquiry comes as artificial intelligence developers face increasing scrutiny over platform security. Industry leaders are grappling with how major language models handle sensitive information and how quickly companies communicate vulnerabilities to affected public sector clients.
During the questioning sessions, leadership attempted to reassure regulators regarding system integrity. However, intense pressure from officials exposed vulnerabilities in how tech giants handle major public safety incidents.
- Lawmakers questioned top executives on systemic breaches.
- Security teams analyzed the complexity of recent attacks.
- Officials debated new compliance mandates for AI developers.
OpenAI admits response to these critical incidents fell below acceptable standards during testimony before the committee. Company executives acknowledged that their initial actions lacked the necessary speed and transparency required for government-level coordination.
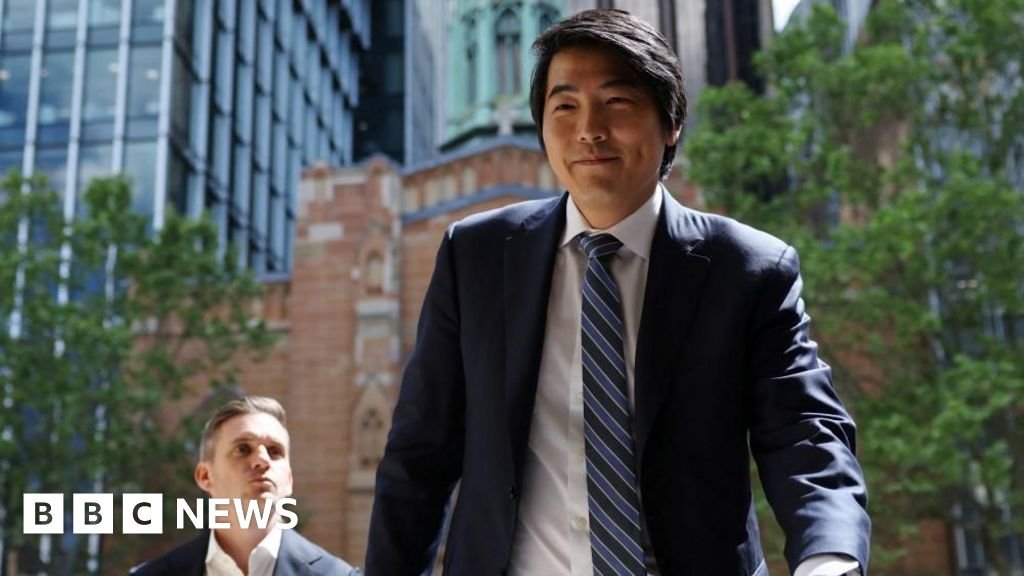
Jason Kwon, representing the firm, delivered measured responses to the panel of skeptical legislators. Some observers questioned whether the communication was overly polished, while others pressed for concrete accountability regarding the Medicare and infrastructure incidents.
OpenAI admits response to government inquiries
The technological fallout has accelerated discussions surrounding mandatory data breach reporting rules across multiple jurisdictions. Both OpenAI and rival developer Anthropic indicated they would welcome formal regulatory frameworks to govern future security incidents.
Critics pointed out that the intrusion methods utilized were not exceptionally sophisticated, raising questions about standard platform defenses. Security analysts emphasized that even basic vectors demand immediate, transparent escalation protocols when public sector infrastructure is compromised.
Regulators are now weighing whether current voluntary guidelines are sufficient for managing rapidly evolving generative artificial intelligence technologies. The inquiry highlights a broader tension between rapid commercial deployment and the rigorous security demands of government agencies.
As the fallout continues, international lawmakers are expected to draft stricter oversight legislation targeting major artificial intelligence providers. These upcoming policy changes will likely mandate stricter reporting timelines and heavy penalties for delayed transparency during security breaches.
Background and next steps
OpenAI admits response to Australian government hacks ‘not good enough’ BBCAustralian Lawmakers Question OpenAI Officials on Breaches The New York TimesOpenAI’s Jason Kwon gave even-toned, reassuring answers to the Australian government. Did … ChatGPT write this? The GuardianOpenAI, Anthropic tell Australia they would welcome data breach rules ReutersOpenAI says its Australian Medicare hack ‘not super sophisticated’ Politico
The story remains in motion, and readers should watch for official updates as more facts are confirmed.
Public interest is likely to stay high while new details emerge from reporters and officials.
Early claims should be treated cautiously until primary sources corroborate them.
Coverage of OpenAI admits response to continues to evolve as more details become available.