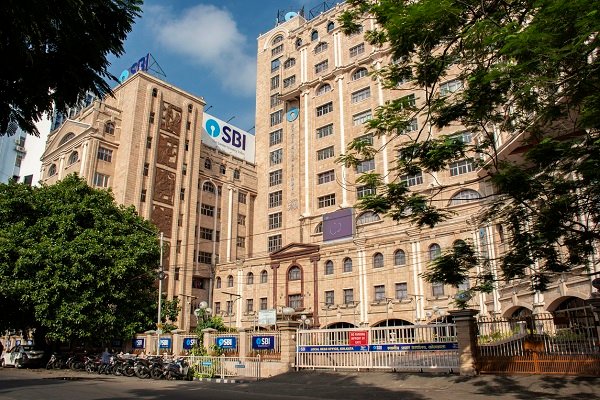


State Bank of India has disclosed a suspected SBI data leak after finding 3,897 records containing personal information on the dark web. The SBI data leak disclosure came in a stock exchange filing on Wednesday, in which the country’s largest public sector lender said it had launched a detailed cybersecurity investigation.
SBI said it received the first alerts on October 16 from three sources: its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team, or CERT-In. Acting on those alerts, the bank examined around 3.75 lakh records circulating on the dark web. In that set, 3,897 entries were identified as containing personally identifiable information, including registered mobile numbers, dates of birth, names, gender, email addresses and residential addresses.
The bank said it had activated its cyber incident response and containment protocols and engaged an independent cybersecurity agency empanelled with CERT-In. The agency will verify the authenticity of the records, trace the source of the potential exposure and assess the security risks for customers and the bank.
How the SBI data leak came to light
The disclosure followed a claim made last week by a threat actor using the name “Siriusim”. In a post on BreachForums, a site known for trading stolen data, the actor claimed to possess 3.75 lakh SBI customer records and 2,722 PDF documents. The claim was flagged on October 16 by the X account CyberPulse56.
The listing described the data as a CSV file with 3.75 lakh rows plus the PDF documents, and the poster shared four sample records as evidence. The Free Press Journal examined the samples and found that the phone numbers were real. Most of the data appeared to relate to loans, while some entries concerned savings account applications and customer acquisition. The claim has not been independently verified.
SBI said the alerts from its threat intelligence provider, the Defence Cyber Agency and CERT-In all pointed to a possible exposure of customer information. Its preliminary analysis of the roughly 3.75 lakh records connected to the SBI data leak then turned up the 3,897 records with personal data.
What the leaked records contain
The exposed information reportedly goes well beyond names and phone numbers. According to the bank’s filing, the identified records included branch and Customer Information File identifiers, lead IDs, and metadata associated with loan and lead records and other related files.
Taken together, the fields in the SBI data leak would give a fraudster enough material to build a detailed profile of a customer. Dhiraj Gupta, the chief technological officer and co-founder of cybersecurity firm mFilterIt, told reporters the leaked information could make scams more convincing. “All of this data will allow fraudsters to build a profile of yours. They’ll be able to target you with precise information and use that to build your confidence,” he said.
SBI has not yet said how many of the 3,897 records can be linked to current customers, and it said a detailed investigation was required to establish the authenticity and completeness of the exposed data and determine the potential source and extent of the exposure.
The SBI data leak response so far
SBI said it had engaged an independent CERT-In-empanelled cybersecurity agency to conduct a comprehensive assessment of the SBI data leak. The bank’s filing said the agency would investigate the nature and extent of the exposure and help with preventive and corrective measures.
The bank also said the incident was not expected to have a material impact on its information technology systems, core business operations, financial performance or business continuity. Core business functions continued to operate normally, the filing said, and the bank said it was closely monitoring the situation and taking measures in line with regulatory requirements.
The SBI data leak disclosure was made under the Securities and Exchange Board of India’s listing obligations and disclosure rules, which require listed companies to inform the exchanges of material cyber incidents.
Fraud risk for customers
The SBI data leak could leave affected customers vulnerable to targeted fraud and social engineering attacks, even if the bank’s core systems and account balances remain secure. Phishing calls and messages that cite real names, branch details and loan information are harder for customers to distinguish from genuine bank communication.
Customers who suspect their details are in the exposed set can watch for unsolicited calls claiming to be from the bank, avoid sharing one-time passwords or card details on incoming calls, and report suspicious messages to the bank’s official channels. The detailed investigation into the SBI data leak and the agency’s assessment will determine the full extent of the exposure.